The Province as a Scam Lab: Why Belfast Should Lead on APP Fraud
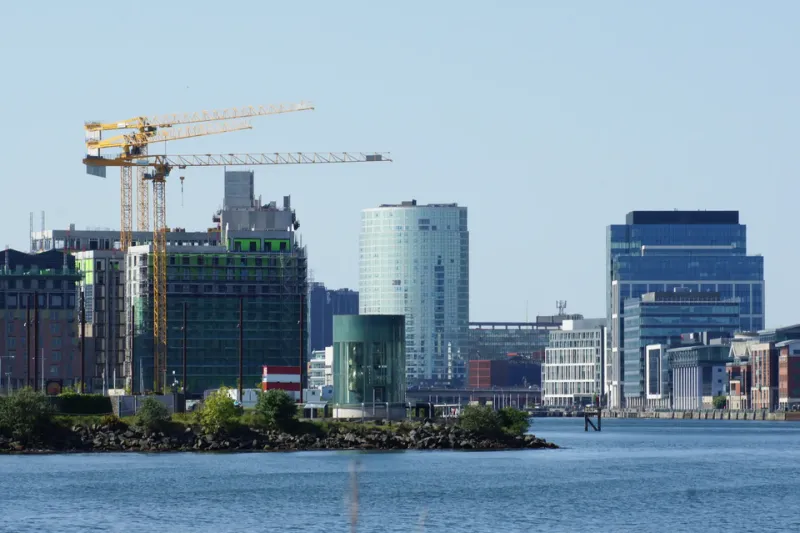
Photo: Davidw1406, CC0, via Wikimedia Commons
Authorised push payment fraud is no longer a niche operational risk. It is a board-level test of whether banks and fintechs can protect customers without turning every payment into a friction-filled ordeal. Since the Payment Systems Regulator's mandatory reimbursement regime took effect in October 2024, the UK has moved from a voluntary code to a compulsory one. In 2026 the argument has shifted: reimbursement is necessary, but it is not prevention.
Fintech NI's view is that Northern Ireland is unusually well placed to become the UK's APP scam lab. Not because the province has more fraud than elsewhere—it does not—but because its banking and fintech sector is small enough to coordinate and close enough to the Border to expose the gaps that a purely domestic strategy misses.
Reimbursement is a floor, not a ceiling
The reimbursement rules have changed incentives. Banks and payment firms now bear more of the cost when a customer is tricked into authorising a payment. That is fairer for victims, and it has forced firms to invest in detection. But reimbursement can also mask the underlying problem. If a scam is reimbursed quickly, the victim is made whole, yet the mule account, the fraudulent website and the social-engineering script may remain active.
Prevention is harder because APP fraud is not a single failure. It can start with a fake investment advert, move through a cloned bank website and end with a genuine payment authorised by a genuine customer. No single firm sees the whole chain. That is why testbeds matter: they allow banks, fintechs, telecoms and regulators to share signals in a controlled environment.
Why Belfast fits the lab profile
Northern Ireland has several advantages. The financial services cluster is compact; senior compliance and fraud leads know each other. The province has strong cyber and data science expertise across its universities and software sector. And the Border creates a natural cross-border dimension that is absent from most UK regions.
That cross-border element is not a footnote. A scam can originate in Dublin, be executed through a Belfast mule account and settle in London. The payment may travel through Faster Payments, SEPA or a card network. A detection model trained only on domestic UK data will miss the Irish leg. A testbed that includes both jurisdictions would be more realistic.
Belfast also has a consumer-protection gap to address. The Financial Ombudsman Service and the PSR operate UK-wide, but cross-border victims can face confusion about which regulator, bank or redress scheme applies. A testbed should map those journeys, not just the technology.
Behavioural biometrics: useful, not a silver bullet
Behavioural biometrics—how a customer types, swipes, pauses and navigates—can spot the difference between a genuine user and a fraudster controlling a session. Belfast has genuine depth in voice and biometrics, and banks already use device and behavioural signals. The technology is promising because it can work in the background without adding friction.
But it is not a silver bullet. Behavioural models can produce false positives, particularly for customers with disabilities, older users or people using unfamiliar devices. They can also be defeated by social engineering, because the victim may be genuinely present and genuinely typing. The testbed should measure not only detection rates but also exclusion, complaint volumes and the time taken to resolve blocked payments.
Mule accounts and the cross-border blind spot
Mule accounts are the plumbing of APP fraud. They are often opened by students, gig workers or people whose identities have been stolen. Detection requires shared intelligence: which accounts receive multiple small credits, which devices log into several accounts, which addresses are reused. Banks are often reluctant to share this data because of privacy and competition concerns.
A Belfast testbed could pilot a trusted mule-detection exchange with clear legal safeguards. Participation should be voluntary, data minimisation should be enforced and an independent evaluator should publish results. The prize is not a central database of suspects. It is a faster way to spot a network before it cashes out.
What a practical agenda would look like
First, a time-limited sandbox involving UK and Irish banks, payment firms and regulators. Second, shared metrics for APP fraud that go beyond reimbursement totals. Third, behavioural biometrics pilots with independent bias testing. Fourth, a cross-border mule intelligence pilot with privacy safeguards. Fifth, consumer education that reaches beyond the usual awareness campaigns.
None of this requires new primary legislation. It requires coordination, funding and a willingness to publish what works and what does not. The FCA and the PSR have sandbox tools; the Central Bank of Ireland has its own innovation hub. A joint Northern Ireland pilot would test whether those tools can speak to each other.
The risk of hubris
There is a danger in overclaiming. Northern Ireland is small, and its fraud patterns may not match those of Manchester or London. A model that works in Belfast may not scale. Privacy advocates will rightly ask why biometric data should be collected at all. Banks will worry about false positives and reputational risk.
Those concerns are arguments for careful design, not for doing nothing. The UK's reimbursement regime is now a fact of life. The next phase must be about prevention, and prevention needs evidence. Northern Ireland can supply that evidence at a scale that is manageable and in a market that is forced to think across a border.
A testbed worth backing
The province does not need to become the UK's fraud capital to become its fraud lab. It needs to be the place where the industry agrees what good prevention looks like, measures it honestly and shares the results. If Belfast can do that, the rest of the UK will have a template—and consumers on both sides of the Border will be better protected.